A FIPS 140-2 Compliant VPN That Runs on Your Own Hardware
A FIPS 140-2 compliant VPN usually arrives as an appliance, which ties the compliance story to one vendor’s supply chain. Speedify combines multiple internet connections in software instead, so a deployment runs on hardware your organization already owns or can source for itself. The open question is the encryption: Speedify does not publish a FIPS 140-3 certificate for its tunnel encryption, so confirm the validation status with Speedify before counting it toward FIPS compliance.
Speedify is software that combines Wi-Fi, 4G/5G cellular, Ethernet, Starlink and satellite internet connections into one faster, more resilient connection, and encrypts the traffic like a VPN. Speedify runs on OpenWrt routers and standard Linux computers, and the Speedify Self-Hosted Server runs on a standard x86_64 Linux host inside your own infrastructure, so the combined traffic stays on hardware you choose. For government contractors, here is what Speedify provides for FIPS compliance, and what to confirm with Speedify first.
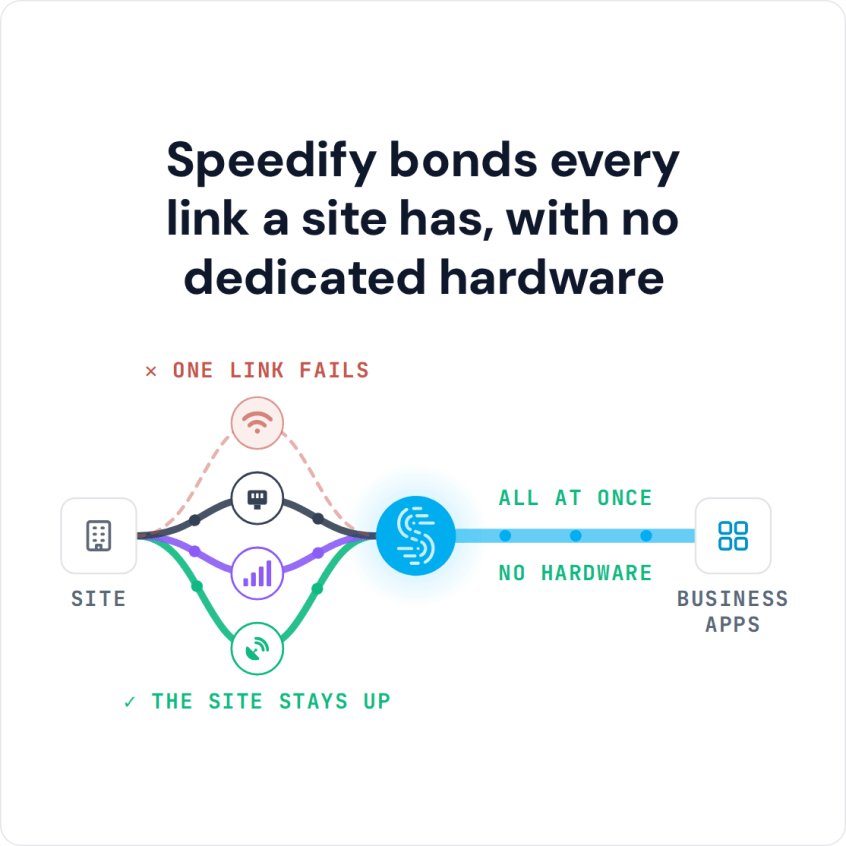
Speedify bonds every link a site has, with no dedicated hardware
Watch now
How Speedify's channel bonding technology works on any hardware
Get started with Speedify for your business
Speedify offers three commercial paths. They're not exclusive — most enterprise customers combine two or more.
01
Speedify Teams
Speedify on every supported OS for every team member
Centralized dashboard for billing, user provisioning, and usage analytics
CSV import/export and a RESTful management API
02
Speedify for Routers
License for supported OpenWrt routers
Powered by Speedify hardware lineup ready to deploy out of the box
Miri, GL.iNET, and other partner models
Whole-LAN bonding without per-device install
03
Embed Speedify into your product
A · DIY
Build it yourself with the Speedify SDK.
Integrate Speedify into your iOS, Android, Windows, macOS, Linux, or QNX product. Full developer documentation, sample code, and supported integration paths. You own the build, we provide the bonding stack.
B · CUSTOM ENGINEERING
Have us build it for you.
The Hardware Lock-In Problem in Compliance Environments
Most solutions for combining internet connections that have a history in government or defense markets were designed as appliances. Peplink’s SpeedFusion requires Peplink or Pepwave hardware on the client side. Cisco SD-WAN is deployable as software but built around Cisco hardware. Fortinet SD-WAN runs on FortiGate appliances. For FIPS-compliant organizations, this creates four specific problems.
- Procurement timelines. Government and defense procurement cycles are long. Proprietary hardware that needs to be purchased, shipped, and cleared through security review introduces delays that commodity hardware running Linux does not. When a field office needs combined internet connections in 30 days, waiting on appliance procurement is not a solution.
- Hardware diversity. Many compliance environments have existing hardware procurement vehicles. An IT team with approved Ubuntu server hardware already in inventory can install Speedify on it without a new procurement action. The same flexibility applies to OpenWrt routers from multiple vendors.
- Supply chain security. Organizations operating under CMMC and similar requirements face growing scrutiny on technology supply chains. Depending on a single vendor to combine internet connections creates a single point of supply chain risk. Speedify’s hardware-agnostic model distributes that risk across a broader hardware ecosystem.
- Refresh cycles. When hardware reaches end of life in an appliance-based deployment, replacing it means buying from the same vendor. In a Speedify deployment, hardware refresh means installing Speedify on the replacement Linux device or router. The same approach makes Speedify an SD-WAN alternative with no dedicated hardware.
Hardware That Runs Speedify: Routers, Linux Servers and Raspberry Pi
Speedify runs on Linux across a range of hardware (routers need a Speedify Router License):
- OpenWrt 23.05 or later routers with x86_64 or aarch64 CPUs, listed GL.iNet routers, and Powered by Speedify routers such as the Miri X510
- Ubuntu 22.04 LTS or later on Intel or AMD x86-64 servers
- Raspberry Pi OS (Bookworm or later) on the Raspberry Pi 5, 4 B and 3B+, and other ARM boards that run a Debian-based Linux
- Any Ubuntu or Raspberry Pi OS compatible device with multiple network interfaces for combining Wi-Fi, 4G/5G cellular, Ethernet, Starlink and satellite connections
Speedify’s Self-Hosted Server runs as a Docker container, installed with Docker Compose, on a Linux host (Ubuntu preferred) with at least 2 x86_64 CPU cores, 4 GB of RAM, 20 GB of storage and a static public IP address. There is no hypervisor image and no vendor-specific VM format: it runs on bare metal or a standard cloud VM and is activated against a Speedify account and Self-Hosted Server license. Full router compatibility details are at support.speedify.com/article/926-what-routers-does-speedify-support.
Speedify on Your Own Linux Hardware vs. Appliance-Based Solutions for FIPS Environments
| Consideration | Speedify for Routers + Self-Hosted Server | Appliance-Based Solutions (e.g., Peplink SpeedFusion) |
|---|---|---|
| Client hardware requirement | Any supported Linux device (OpenWrt, Ubuntu, ARM Linux) | Vendor-specific hardware required at each endpoint |
| Server hardware requirement | Any x86_64 Linux server or cloud VM with Docker and a static public IP | FusionHub virtual appliance or vendor hardware |
| Procurement flexibility | High: source hardware from any compatible vendor | Low: tied to vendor’s product line |
| Air-gap / isolated network compatibility | Not documented: the server is activated against a Speedify account and license; confirm offline use with Speedify | Partial: some configurations require vendor infrastructure contact |
| Connection types combined | Wi-Fi, 4G/5G cellular, Ethernet, Starlink and satellite | Wi-Fi, 4G/5G cellular, Ethernet, Starlink and satellite |
| FIPS compliance path | No published FIPS certificate: Speedify’s encryption uses Google’s BoringSSL; confirm current status with Speedify | Via Peplink FIPS Module (CMVP #4763, FIPS 140-2 Level 1), moved to the CMVP Historical List on 9/21/2026 with all FIPS 140-2 certificates; check the NIST database for a current FIPS 140-3 certificate |
| Deployment complexity | Speedify install on the client, Docker container on the server | Virtual appliance provisioning + Peplink hardware configuration |
The Compliance Case for Speedify’s Self-Hosted Server
Speedify’s Self-Hosted Server ends the combined, encrypted traffic on a server your organization manages, so compliance-critical traffic does not pass through Speedify’s shared server network. Device sign-in and server activation still use Speedify’s account service. Three compliance conversations this simplifies:
- Data residency. Combined traffic ends at a server in the data center, VPC, or network boundary the organization controls. For organizations with data residency requirements (ITAR-controlled technical data, HIPAA-covered information, CUI), this matters directly.
- Audit boundary. When the Speedify Self-Hosted Server sits inside the organization’s compliance boundary, the server that combines your connections is part of the system under audit rather than a third-party dependency requiring its own assessment.
- Incident response. When the server is on infrastructure the organization owns, incident response teams have direct access to logs, network flow data, and server state.
For more details on Speedify’s server deployment options, see the Speedify server infrastructure page.
FIPS 140-2 vs. FIPS 140-3 for New Deployments
All FIPS 140-2 certificates moved to the NIST CMVP Historical List on September 21, 2026, so new procurements now look for FIPS 140-3 validated modules. Speedify’s tunnel encryption uses Google’s BoringSSL rather than the operating system’s cryptographic module, and Speedify does not publish a FIPS 140-3 certificate, so ask Speedify for the current validation status before you buy.
Getting Started with Speedify for FIPS Environments
Speedify’s sales team works with IT managers, network engineers, and compliance teams at contractors and government-adjacent businesses. To discuss deployment requirements, compliance environment specifics, or hardware compatibility for a specific network project, contact Speedify.
Speedify Business Solutions
Speedify Teams
Speedify for Routers
Speedify Embedded Solutions and Integrations
Embed Speedify software into your app or hardware products and leverage the core channel bonding technology of Speedify in new and interesting ways.